WHAT IS THE NIS 2 DIRECTIVE?
The NIS2 Directive has been mandatory since October 2024 and aims to strengthen cybersecurity requirements for essential and important entities, particularly in industry, critical infrastructure, and public services.
SERMA Safety and Security provides comprehensive support to guide organizations through their compliance journey, assessing their current security posture and delivering tailored solutions that address the specific requirements of the directive.
Do you know your level of compliance?
OUR SUPPORT
1
Assessment of the current environment
Option 1
- Gap analysis and roadmap
- Executive team awareness training
Offering starting at €4.000
Our offering includes:
- Gap analysis
- Development of a compliance roadmap, taking into account your company’s resources and priorities.
Option 2
- Gap analysis and roadmap
- Executive team awareness training
Offering starting at €8.000
Our offering includes:
- Half-day cybersecurity awareness session for executive teams
- Mapping of regulated information systems (SIR)
- Justification of exemptions for non-regulated information systems
- Gap analysis (Option 1)
- Development of the compliance roadmap (Option 1)
2
Compliance support
(CISO as a service)
We support you every step of the way in implementing the initiatives identified through the gap analysis, while ensuring compliance with the priorities and deadlines established in the roadmap.
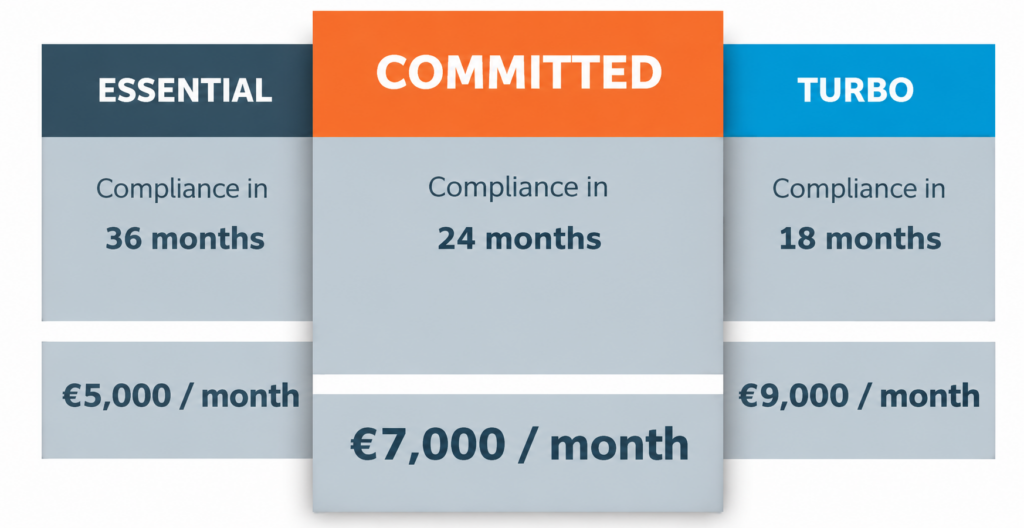
Additional Options: Partnerships with specialized law firms and cybersecurity solution providers to ensure comprehensive coverage of NIS2 requirements.
3
PASSI compliance audit
Our auditors, independent from the consulting team, conduct PASSI-qualified compliance audits in strict accordance with the applicable framework.
If no major non-conformities are identified, the audit report provides a presumption of compliance with the NIS2 Directive.
A summary version of the report can also be shared with third parties to demonstrate your compliance.

ANSSI Security Certification covering the five scopes of the PASSI framework (Penetration Testing / Organizational and Physical Security Audits / Configuration Audits / Architecture Audits / Code Audits).
To explore further
Discover our case studies and resources dedicated to our Directive NIS 2 services