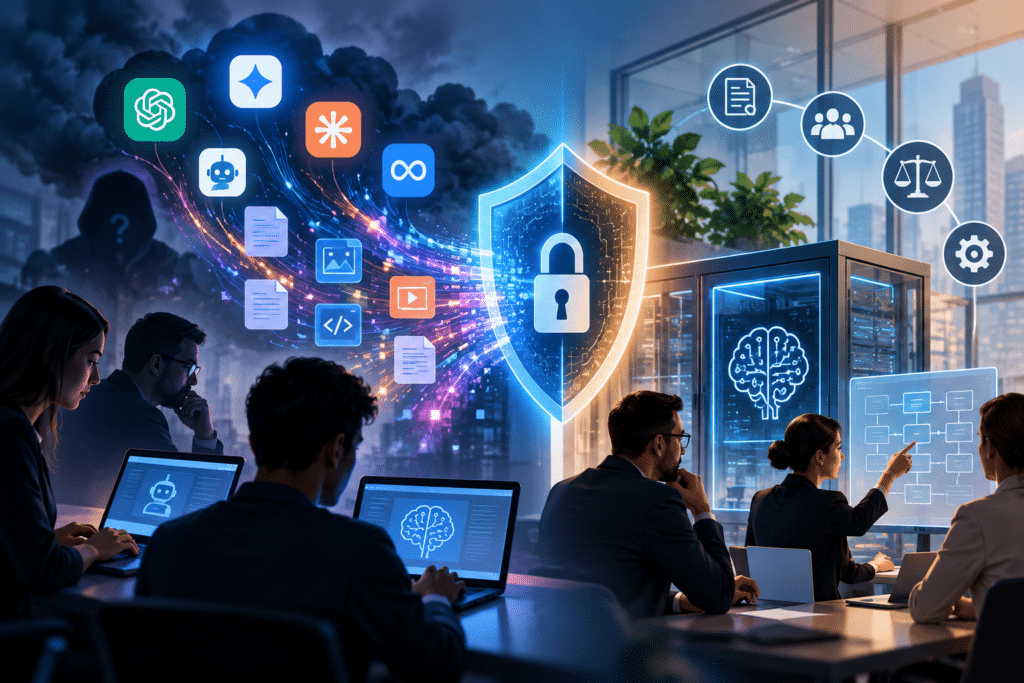
Since the emergence of large language models (LLMs) such as ChatGPT, Gemini, Claude, and open-source artificial intelligence (AI) solutions, their adoption in professional environments has grown at an almost uncontrolled pace. This rapid uptake has introduced a new risk for businesses: the intentional or unintentional disclosure of sensitive information through AI tools.
This phenomenon, known as Shadow AI, is transforming data governance and presenting Chief Information Security Officers (CISOs) with an unprecedented challenge: regulating the use of these technologies without unnecessarily hindering innovation.
This article provides a comprehensive analysis of AI-related risks, an overview of the different types of AI models and their implications, and an in-depth examination of the issue from a Governance, Risk and Compliance (GRC) perspective. It concludes with potential strategic approaches, an analysis of the Digital Operational Resilience Act (DORA), and a series of operational recommendations for adopting AI responsibly, securely and in compliance with applicable regulations.
Understanding AI and Its Different Forms
Artificial intelligence is not a homogeneous technology. Businesses use various types of AI models, each presenting distinct risks.
Conversational text-based AI systems, such as ChatGPT, Gemini, Copilot and Claude, are the most widely used. They enable users to draft documents, analyse data and automate tasks, but they may also process sensitive information entered directly by users. When a company does not control or secure these tools, the primary risk lies in the transmission of confidential data to a third-party provider.
Multimodal AI introduces an additional layer of complexity. These systems can process not only text but also images, videos, PDF documents and code snippets. Their ability to analyse entire files significantly increases the potential exposure of sensitive information. A single document shared by an employee may contain metadata, confidential information, personal data or strategic information that the user may not even be aware of.
Open-source or self-hosted AI systems represent another specific case. In theory, they can provide a high level of control, but they require local management of models, datasets (structured collections of data used to train, validate and test models), logs and infrastructure. In practice, many businesses lack the maturity, technical capabilities or resources needed to maintain a secure environment. The risk no longer primarily stems from outsourcing data processing, but from internal security weaknesses and misconfigurations of locally hosted platforms.
Finally, specialised AI solutions (legal, HR, medical, software development, marketing, etc.) sometimes incorporate their own learning or data analysis mechanisms. These tools create uncertainty around data hosting, training and the reuse of information submitted by users. It is often difficult to determine precisely where data is stored, how it is used to improve the model, and whether it may be shared or reused by the provider.
This lack of transparency complicates risk assessments and the implementation of robust contractual safeguards. Their use therefore exposes businesses to specific risks related to the provider’s business model (such as indirect data monetisation or dependence on a proprietary service) and limited visibility into the product’s technical data management practices. These factors may lead to regulatory compliance issues or inadequate protection of sensitive information.
Given the diversity of these models, it is becoming increasingly difficult for Chief Information Security Officers (CISOs) to establish a common framework applicable to all AI solutions. AI-related risks are not uniform: they depend on the model, hosting arrangements, provider, types of data processed and level of internal adoption.
The Rise of Shadow AI: A New Form of Unintentional Data Exfiltration
One of the most critical challenges emerging with artificial intelligence is Shadow AI.
Like Shadow IT before it, Shadow AI refers to the use of tools that have not been approved by the organisation. However, its potential impact is considerably greater, as these tools process not only data itself but also its context, structure and meaning.
Across many organisations, employees use AI to save time on activities such as drafting emails, translating internal documents, generating code, analysing contracts or preparing strategic presentations.
Without appropriate training or explicit governance, and in a context where many organisations have yet to establish clear policies regarding AI use, employees are often unaware that entering non-anonymised text, database extracts or internal procedures may result in the disclosure of trade secrets to external platforms.
Some platforms temporarily retain data for debugging or model improvement purposes, potentially resulting in breaches of regulatory obligations relating to personal data protection or confidential information.
This risk is amplified by the immediate, largely invisible and difficult-to-trace nature of these interactions.
Unlike traditional data leaks, Shadow AI does not necessarily leave explicit network logs and may go entirely undetected by security tools and Security Operations Centres (SOCs).
It is now considered an emerging source of unintentional data exfiltration within organisations.
Strategic Options for Businesses: Ban, Allow or Regulate AI?
Faced with this phenomenon, business leaders and CISOs must choose between three main strategic approaches.
Some organisations opt for a complete ban on AI tools, adopting a maximum-risk-avoidance strategy. However, this approach often creates operational frustration and encourages the covert use of unauthorised or parallel tools. Organisations pursuing this strategy deprive themselves of a major source of innovation while potentially generating even more difficult-to-detect Shadow AI activities.
Others choose unrestricted adoption, allowing generative AI to be used without meaningful limitations. Although this strategy can accelerate productivity, it relies heavily on trust in providers and assumes that employees will automatically behave responsibly. In practice, it exposes organisations to significant legal, regulatory, contractual and operational risks.
Most organisations with structured IT governance favour a hybrid approach.
Under this model, AI use is permitted, but only for specific user profiles, clearly defined use cases and through platforms controlled by the organisation.
This approach may be supported by internal AI platforms, enterprise proxies, acceptable-use policies, appropriate confidentiality clauses and automated filtering mechanisms.
Although this strategy requires robust governance, it offers the most balanced approach to reconciling innovation and security.
AI Governance, Risk and Compliance (GRC) Challenges
AI must be addressed through a Governance, Risk and Compliance (GRC) framework.
From a governance perspective, organisations must define clear policies, identify roles and responsibilities, establish usage controls and develop a structured documentation framework to ensure that decisions can be traced and justified.
Without an established framework, AI adoption becomes unregulated and impossible to supervise effectively.
From a risk management perspective, AI introduces new threats while exacerbating existing vulnerabilities.
A lack of user awareness may lead to the unintentional transmission of sensitive information to external providers.
AI may also generate inaccurate or fabricated responses, negatively influence the outputs of automated systems, and increase technological dependence on specific providers, making organisations more vulnerable to service disruptions or changes in supplier practices.
Risk assessments must therefore be updated to incorporate these new threat vectors and reflect actual business usage.
Compliance is equally central to this issue.
The General Data Protection Regulation (GDPR), DORA, NIS2, sector-specific obligations, internal hosting requirements and contractual commitments establish a strict framework for AI use.
Businesses must identify the personal data involved, applicable processing clauses, technical and organisational safeguards, data storage locations and deletion mechanisms.
They must also anticipate audits and demonstrate their ability to exercise effective control over the AI models they use.
AI and DORA: A Key Regulatory Framework
The Digital Operational Resilience Act (DORA) strengthens the responsibilities of financial entities regarding the security of their information systems and third-party service providers.
In the context of AI, this creates several significant obligations.
An organisation subject to DORA must demonstrate that it effectively manages the risks associated with its service providers, including AI vendors.
If an externally hosted model processes critical data or application code, the organisation must be able to assess the potential impact on business continuity, operational risks and data protection.
DORA also requires structured and rigorous incident management.
However, when a data leak occurs through a prompt or a document submitted to an AI system, tracing the incident can be extremely difficult or even impossible.
This significantly complicates incident detection, investigation and reporting.
The regulation also requires organisations to strengthen their operational resilience, raising concerns about dependence on external AI providers.
A service outage or sudden change in contractual terms could have an immediate and potentially critical impact on business operations.
Consequently, integrating AI into the DORA compliance framework requires more than a specific risk assessment.
It involves accurately identifying the AI models used, the data they process, the providers involved and the associated risks, as well as conducting compliance audits, monitoring contractual commitments and implementing continuous supervision mechanisms.
Organisations that simply authorise external AI tools without incorporating these requirements into their DORA framework risk significant regulatory non-compliance.
Technical and Organisational Solutions for Controlled and Secure AI
Implementing secure AI relies on several key pillars.
The first step is to establish a controlled usage architecture.
This may include an internal proxy capable of filtering prompts, masking sensitive information or implementing automated anonymisation mechanisms.
Dedicated solutions can help ensure that personal or confidential information is not transmitted in plain text.
The implementation of secure AI relies on several key pillars. The first step is to establish a controlled usage architecture.
This may include an internal proxy capable of filtering prompts, masking sensitive information or implementing automated anonymisation mechanisms.
Dedicated solutions, such as Data Loss Prevention (DLP) tools applied to AI data flows, enterprise AI platforms incorporating encryption capabilities, or security gateways capable of analysing and sanitising data before transmission, can help ensure that personal or confidential information is not transmitted in plain text.
The second pillar concerns control over AI platforms.
Organisations can choose commercial AI solutions supported by enhanced contractual safeguards or internal AI systems hosted within controlled environments, thereby creating a secure ecosystem for AI use.
User training is another essential pillar.
Trained employees understand which types of information may or may not be submitted to AI tools, recognise the associated risks and develop appropriate security practices.
Supervision mechanisms must also be implemented, including usage logs, request monitoring and alerts triggered by abnormal behaviour.
Finally, specific contractual clauses should be introduced, covering the prohibition of model training on company data, data storage locations, immediate data deletion, incident traceability and enhanced confidentiality guarantees.
GRC Solutions: Policies, Processes and Controls
From a GRC perspective, implementing secure AI requires a robust documentation framework.
An AI acceptable-use policy must be developed and communicated to all employees.
This policy should specify which data may be processed, which use cases are permitted, which tools are approved and which activities are explicitly prohibited.
It should be supported by detailed procedures, particularly those covering prompt reviews, incident management and contractual arrangements with AI providers.
Risk assessments must incorporate AI models, vendors, processed data and potential impacts.
Continuous controls should be implemented to verify compliance with best practices and identify deviations.
Finally, organisations should establish an audit plan to periodically assess whether their AI usage complies with internal policies and applicable regulatory obligations.
Conclusion
Artificial intelligence offers businesses major opportunities to improve efficiency, automate repetitive tasks, accelerate content production and support decision-making.
However, it also introduces significant risks of data leakage, challenging traditional approaches to governance and security.
Without appropriate policies, controls and training, AI can become a channel for the unintentional exfiltration of sensitive information and a critical vulnerability within an organisation’s information systems.
As with any emerging technology, the challenge is not to prohibit AI but to maintain control over its use.
Businesses must adopt a balanced strategy combining innovation, security, compliance and governance.
Those that succeed will be the organisations capable of establishing a clear, documented, controlled and auditable framework.
In this context, CISOs, Data Protection Officers (DPOs), GRC managers and senior leadership play a central role in transforming AI from an emerging threat into a sustainable driver of business value.